Agentic SOC with sovereign AI
Cybersecurity and cyber intelligence in a single platform.
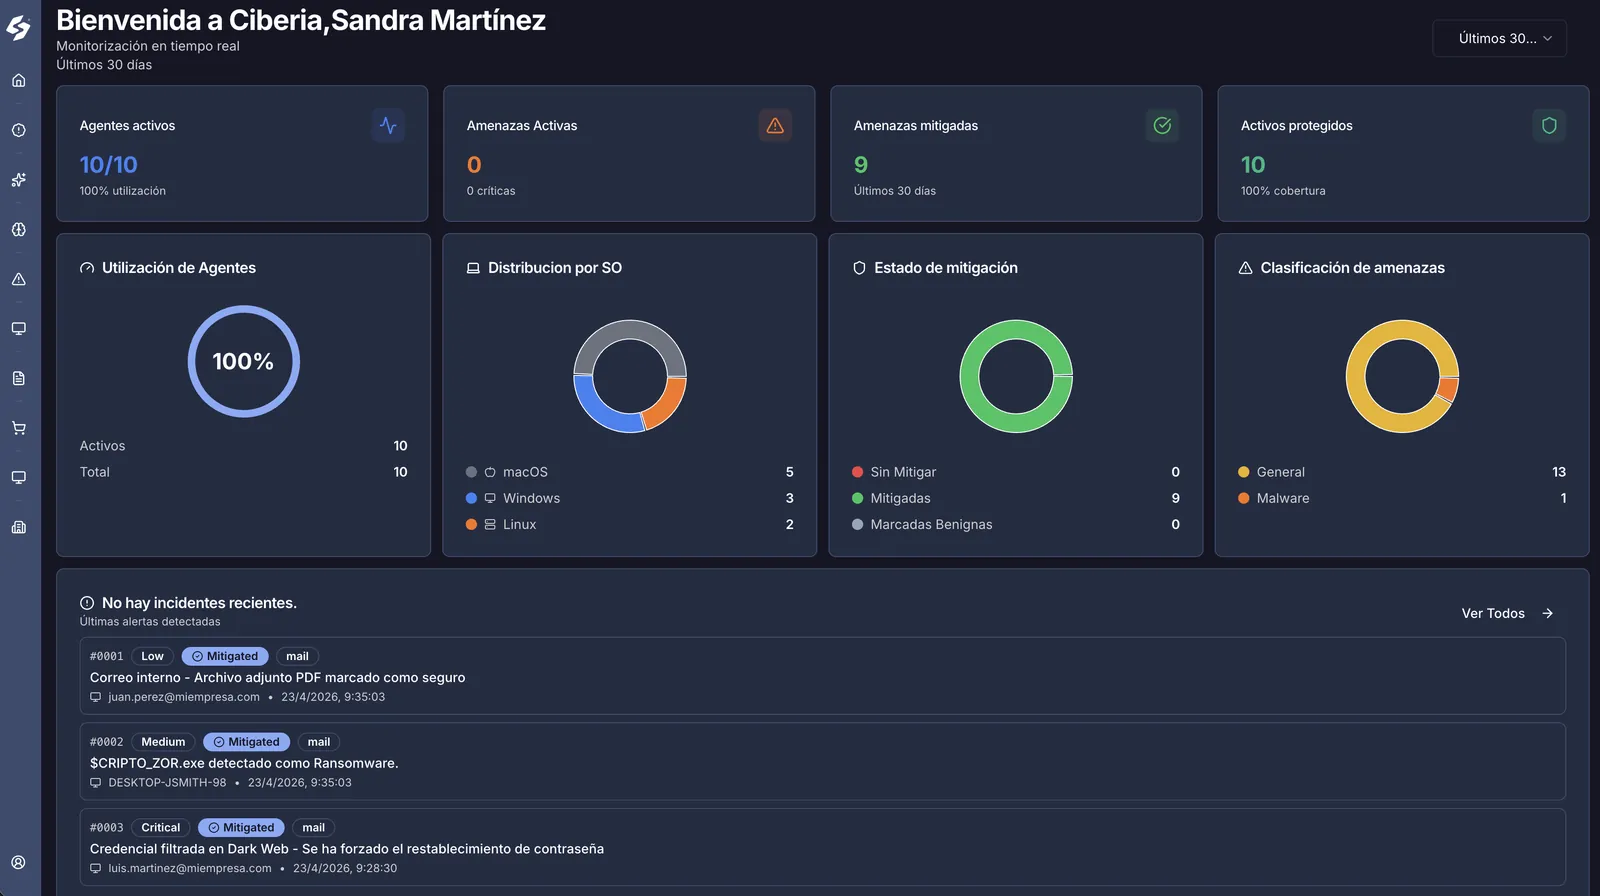
Already have EDR, SIEM, firewall or email? Ciberia integrates with your systems, automates triage with its own AI and responds 24/7.
 Ciberia AI SOC Platform
Ciberia builds on the technology you already have.
600+ integrations across EDR, SIEM, firewall, email, identity and cloud. Nothing gets replaced. Ciberia adds detection, context and response on top.
The traditional SOC no longer scales.
- Volume
- Alerts grow faster than the team. The serious ones get handled and the rest pile up unreviewed.
- Talent
- Covering 24/7 takes shifts and handovers. Retaining analysts keeps getting more expensive, and knowledge leaves with the people.
- Time
- Hours go by between an alert firing and someone acting on it. After hours, that window gets longer.
The quick fix is to automate with third-party AI, at the cost of your telemetry leaving your organization. At Ciberia, we don't accept that trade-off.
One platform. Four products that feed each other.
Alerts from your tools flow into Ciberia and are cross-checked against intelligence, hunting and exposure monitoring.
Threat intelligence
Ciberia Intel
Threat actors, campaigns, malware families, vulnerabilities, IOCs and reports, from our own intelligence and third-party sources.
Proactive hunting
Threat Hunting
Our agentic system looks for what is already inside and has not triggered any alert, with hypotheses based on MITRE ATT&CK.
Agentic SOC 24x7
Ciberia MDR
Proprietary AI agents investigate every alert from endpoint, network, email, identity and cloud, and an analyst validates every response.
Credentials, infostealers and dark web
Ciberia CTM
Leaked credentials, infostealers, the dark web and forums: what circulates about your organization outside your network.
What intelligence uncovers guides the hunting. What hunting finds becomes new detection rules for Ciberia MDR.
- 1Intel
- 2Hunting
- 3MDR
- 4New rules
Follow an alert.
How Ciberia handles an identity alert in the early hours, in five steps.

Sunday02:47:12
Sunday, 02:47.
Okta logs a sign-in by your CFO from a country where your company doesn't operate. On Friday she signed in from Madrid.
Context in seconds.
In eight seconds, Ciberia checks the alert against its intelligence, the account's exposure and her laptop. All three signals point the same way.
AI proposes. An analyst decides.
CiberIA rates the risk as high and proposes three actions. The on-call analyst reviews the evidence and approves them.
Contained.
The actions run on your tools, one at a time and fully logged. A ticket is opened and the owner is notified, within the 15-minute SLA.
And it learns.
Threat Hunting looks for the same pattern across every other account, and tonight's incident becomes a new detection rule.
At 02:47 your team slept. Ciberia didn't.
See how the platform works
Compared with a traditional SOC.
15min
Contractual response SLA: from critical alert to initial containment.
| Aspect | Traditional SOC | Ciberia |
|---|---|---|
| Triage | Manual, with a queue that keeps growing | 90% automated |
| Coverage | Shifts and handovers | 24/7 with no blind shifts |
| Response time | Hours to contain | Containment in minutes |
| Scaling | Hire more analysts | Doesn't depend on adding headcount |
Your data, under control.
This is sovereign AI: we process information on servers located in Spain, with AI models built on our own architecture, and nothing goes through third-party LLMs. And we do it with two certifications: Spain's National Security Framework (ENS), High category, and ISO/IEC 27001.
 CertifiedENS High CategoryCertification of conformity with Spain's National Security Framework (ENS), High category.
 CertifiedISO/IEC 27001Information security management system certified to the ISO/IEC 27001 standard.
Our own intelligence
Ciberia Intel draws on our own and third-party cyber intelligence, and runs on our infrastructure.
Data under control
Information is processed locally and stays in Spain.
Every decision is traceable
Every automatic action leaves a record: who took it, when, on what criteria and on what data.
Under attack right now?
Disconnect the affected devices from the network, don't delete anything and get help. We explain what to do in the first hours.
Frequently asked questions
What is Ciberia?
Ciberia is a Spanish cybersecurity and cyber intelligence company. Its platform brings together four products: Ciberia Intel (threat intelligence), Threat Hunting, Ciberia MDR (Agentic SOC 24x7, with proprietary AI agents and analysts who validate) and Ciberia CTM (leaked credentials, infostealers, the dark web and forums).
Do I have to change my security tools?
No. Ciberia integrates with what you already use (EDR, SIEM, firewall, email, identity and cloud) and works on that telemetry. It does not replace your EDR or your SIEM.
Where is my data processed?
On servers located in Spain. The AI models are built on our own architecture, and your telemetry is not sent to third-party LLMs.
Does the AI make decisions on its own?
The AI automates triage and proposes actions. An analyst validates what matters, and every automatic action leaves a record: who took it, when, on what criteria and on what data.
Which security certifications does Ciberia hold?
Ciberia holds the certification of conformity with Spain's National Security Framework (ENS) in the High category, the most demanding level of the framework, and its information security management system is certified to ISO/IEC 27001. If your organization works with the public sector or with suppliers that require it, we walk you through the details in the first meeting.
What is the difference between EDR and MDR?
EDR is a tool that detects and blocks threats on endpoints. A traditional MDR is a service that monitors those signals in shifts. Ciberia MDR does that work 24x7 with AI agents and analysts who validate, on top of your EDR and without replacing it.
What should I do if I'm under a cyberattack right now?
Disconnect the affected devices from the network, don't delete anything and contact an incident response team. Our incident response page covers the steps for the first hours and how to ask us for help.
Let's talk about your security.
We show you the platform with your technology in mind and look at what we can automate from day one.